Security · Hosting & Maintenance
PHP2ShellSerious security flaw in PHP — what website operators need to know now
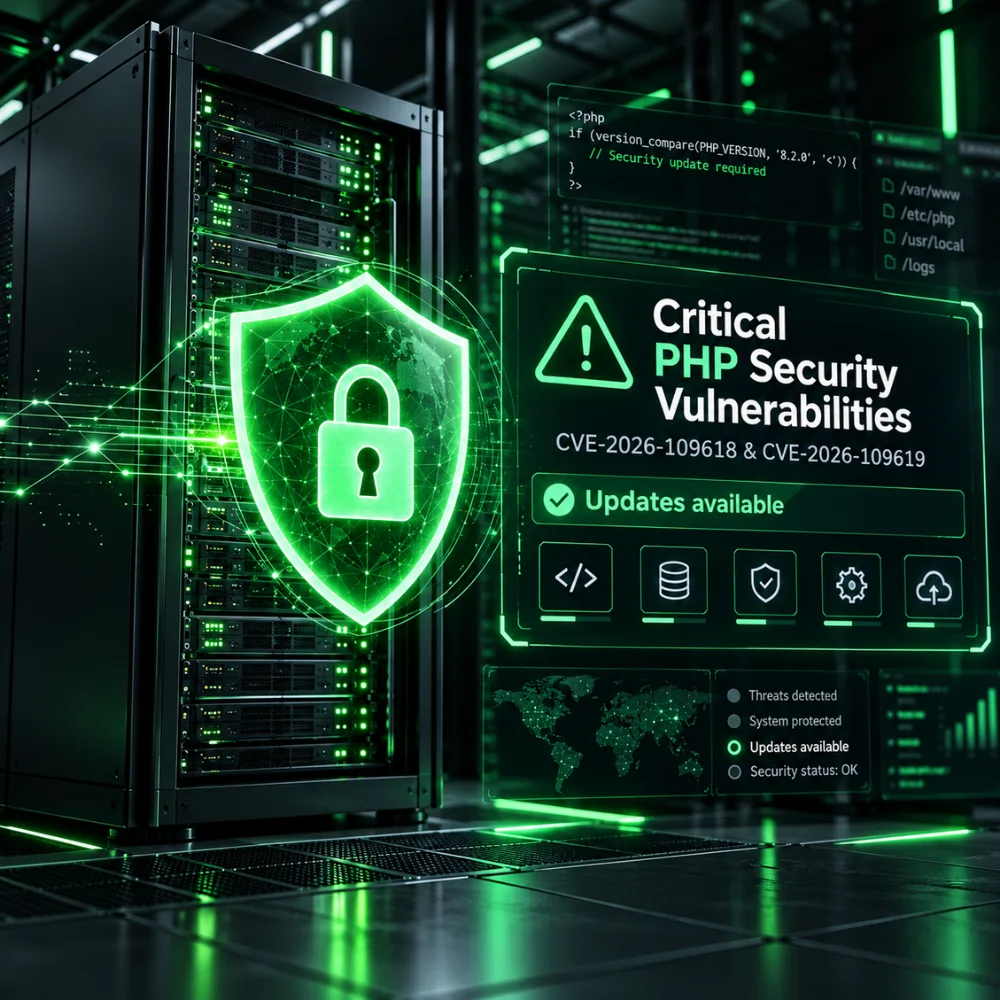
On October 21, 2026, two serious security vulnerabilities were discovered in PHP — the technology on which most websites, including almost all WordPress sites, run. Hackers can use this to take control of a website. The good news: An update is already available. Here you can read in an understandable way what this means for you and what to do about it.
- What
- Two gaps in PHPtogether called „PHP2Shell“
- Danger
- Critical9.2 out of 10 points, BSI warning level Orange
- Affected
- Around 70 of % all websitesEveryone who runs PHP — including WordPress
- Solution
- PHP updateis already available
Status: October 23, 2026. The situation continues to evolve. The current information from the PHP project and the BSI are decisive.
The most important in a nutshell
PHP is the programming language that runs in the background of most websites — much like the engine of a car. You don’t see it, but without it nothing runs. Exactly in this engine two serious errors were found.
- Attackers can take control of a website — without password and without you noticing it at first
- Almost every website that runs on PHP is affected: WordPress, WooCommerce, Shopware, TYPO3, Joomla, and many more.
- There is already one Update that closes the gaps
- The Federal Office for Information Security (BSI) explicitly warns and advises immediate action.
- Criminals are already specifically looking for unprotected websites
If you only do one thing
Ask your hoster or web agency today: „Is the PHP update against PHP2Shell installed on my website?“ It is best to have the answer confirmed in writing.
What happened?
Security researchers have discovered two flaws within PHP. Collectively, they are known as „PHP2Shell“ (official identifiers: CVE-2026-109618 and CVE-2026-109619).
Put simply: An attacker calls your website with a specially prepared request — similar to how a browser opens a page. Through the error in PHP, he can then execute his own commands on your server. He doesn’t need a password for that.
A comparison from everyday life
Imagine that it’s not your own door lock that’s broken, but a lock model that the manufacturer has installed in millions of homes. How carefully you lock it won’t matter then. The solution is an improved lock from the manufacturer — that’s exactly what the PHP update is about.
What attackers can do
Stealing data
Read customer data, orders, and passwords — in case of emergency with reporting obligations under the GDPR.
Change the website
Insert malicious software, spam, or links to other sites. Google and browsers then warn about your website.
Hinder website
The website or shop is no longer accessible — with dire consequences for sales and reputation.
Install the backdoor
Create a hidden access point that will remain after the update.
Why the rush? The BSI expects that large-scale attacks will begin within a few hours after the updates are released. Several authorities, clinics, and hosting companies have taken their websites offline as a precaution until everything is secured.
Is my website affected?
If your website runs on WordPress, WooCommerce, Shopware, TYPO3, Joomla or an individually programmed PHP solution, then yes — as long as the update hasn't been installed. The theme, plugins, or WordPress version do not play a role here. The only thing that matters is the PHP version on the server.
| Your PHP version | Protected from | Status |
|---|---|---|
| PHP 8.5 | 8.5.12 | Update available |
| PHP 8.4 | 8.4.27 | Update available |
| PHP 8.3 | 8.3.36 | Update available |
| PHP 8.2 | 8.2.35 | Update available |
| PHP 8.1 and older | only emergency corrections | Obsolete |
If you are still using PHP 8.1 or earlier, switching to a current version is in any case overdue. Many hosting providers also provide their own customized PHP versions — the number may then differ slightly from the table. If in doubt, ask about it.
How to find your PHP version
- In WordPress: Tools → Website Status → Report → Server
- In your host's control panel, usually under „PHP settings“ or „PHP version“
- Or simply: Ask your hosting provider or web agency
No interest in technology? We’ll take care of it.
Synext IT checks your PHP version, downloads the update or clarifies it with your hosting provider, and then checks your website for any issues.
What you should do now
For most website operators, it consists of three steps. The technical part is usually handled by your hosting provider or agency.
Have the update confirmed
With a hosting package, the provider is responsible for the update. Don’t just ask, „Is everything secure?“ but ask specifically about the following: PHP version number. Many professional hosts have already installed the update.
Include all websites
Also consider secondary sites: old test pages, a second domain, an old shop. Especially forgotten installations are a popular entry point.
Have abnormalities checked
The update closes the door — anyone who has already logged in before will still be able to stay in. Check for unknown administrator accounts, changed files, or strange redirects. If you suspect anything: change all passwords and prepare a clean backup.
Changing settings is not enough
Tips are circulating online that aim to reduce the vulnerability through individual settings. This only makes attacks more difficult. According to the PHP project and the BSI, only the update will help.
For your administrator: technical notes
Check the version:
php -v
php-fpm -v- After updating PHP-FPM or restarting the webserver — otherwise, running processes will continue to use the old code. Then check the version again.
- Affected are PHP-FPM, Apache with
mod_php(highest risk), php-cgi, FrankenPHP and LiteSpeed — according to the BSI back to at least PHP 5. - In distribution or hosting packages, the package version counts, not the number from php.net. For 7.4, 8.0 and 8.1, there are source code backports.
- INI adjustments (e.g.
session.upload_progress.enabled) And WAF rules are only a temporary solution, not a replacement for the update.
Checklist: Is your website protected?
Skip the things that have already been done. This way, you can see at a glance if there’s anything left to do.
Your checklist
0 out of 5 completed
Frequently Asked Questions
Is it enough to update WordPress and all the plugins?
No. The flaw is not in WordPress, but in PHP on the server. WordPress and plugin updates do not change this. The update of PHP itself is necessary — with a hosting package provided by the provider.
My hoster takes care of everything. Do I still have to do anything?
Yes, but only a small amount: Please confirm the update with the version number. Many hosting providers have already responded — a brief inquiry will give you certainty and confirmation for your documents.
How do I know if my website has already been attacked?
Warning signs include unknown administrator accounts, suddenly changed content, redirects to external sites, or warnings from Google or your browser. However, in many cases, an attack from the outside is not visible. If you suspect something is amiss, change all passwords and have a professional company check them.
Can Synext IT take over this for me?
Yes. We check the PHP version of your websites, install the update or coordinate with your hosting provider and then check for any issues. Upon request, you will receive a written confirmation. If your website is hosted by Synext IT, the update is already complete.
Sources
- PHP Project: Security notice and updates from October 21, 2026, php.net
- BSI: Cyber security alert regarding PHP, BITS-H No. 2026-297981-1032, bsi.bund.de
- Wiz Research: Analysis on PHP2Shell, wiz.io
- CERT-EU: Advisory regarding CVE-2026-109618 and CVE-2026-109619
All information is based on the best available knowledge as of October 23, 2026. This article does not replace individual safety advice.
Next step
Update available. Have it backed up now.
Don't want to deal with the technical side yourself? We'll review your website, check the status with your hosting provider, and secure it — on short notice.
- Short-term review of your website
- Update and coordination with your hosting provider
- Written confirmation of your documents
Performance
Maintenance & Hosting
Updates, backups, monitoring, and quick assistance in case of security incidents — so that the next breach doesn’t become an emergency.
View servicessynext-it.de · Response within 24 hours
 English
 German